Trezor Data Breach Exposes 27K Customer Orders
Trezor confirms a data breach at shipping partner Skladon affecting 27,000 orders, exposing customer contact and delivery details and triggering new privacy measures.
Trezor has disclosed a data breach involving Skladon, one of its shipping partners, after an attacker gained unauthorized access to customer order information. Disclosed on November 15, 2026, the incident potentially exposed information linked to approximately 27,000 orders placed between August 9 and November 7.
Although Trezor's own systems and hardware wallets were not compromised, the leaked information has raised concerns about fraudulent calls, customer privacy and the handling of personal data by third party delivery providers.
Skladon Breach Exposes Personal Details From 27,000 Orders
According to Trezor's official announcement, Skladon notified the company on November 15 that an attacker had accessed and exported order information stored within its systems.
The compromised records relate to orders placed between August 9 and November 7, 2026. The exposed information includes customers' names, phone numbers, residential addresses, email addresses and order details.
The incident involves approximately 27,000 orders, with affected customers spread across multiple countries. Since Skladon handles deliveries for Trezor in several international markets, the exposure is not restricted to a single region.
Trezor clarified that its internal systems were not breached and that the incident did not compromise customers' hardware wallets. The security issue originated within the shipping partner's environment rather than Trezor's own infrastructure.
Customers Face Fraudulent Calls & Physical Security Risks
Following the exposure, customers in multiple countries outside the United States reportedly received scam calls using information connected to their orders.
The leaked combination of names, telephone numbers, addresses and purchase details gives scammers information they could use to make unsolicited communications appear legitimate. Knowledge of a customer's hardware wallet purchase could also help attackers create convincing impersonation attempts.
Trezor has advised customers to treat unexpected calls, text messages, emails and letters about their orders as suspicious. The company has specifically warned about potential physical security risks associated with exposed residential addresses.
It also reminded customers that Trezor will never initiate unsolicited phone calls or ask anyone to disclose their wallet backup.
Customers who received Trezor's November 15 notification and ordered between August 9 and November 7 are included in the reported incident. A smaller group of customers who placed orders between August 9 and August 14 may also be affected. However, Trezor cannot directly email these customers because their information had already been anonymized in its systems.
Customers in the United States are not affected because Skladon does not provide shipping services there.
Data breach involving Skladon
On 15 November, Skladon, one of our delivery partners, notified us that an attacker had gained unauthorized access to Trezor order data it holds. We’re still investigating with Skladon, but we want to let you know now.
What we know:
• We believe the data for about 27,000 orders placed between 9 August and 7 November was exported.
• It includes name, phone number, address, email and order details.
• Skladon delivers to many countries, so this isn’t limited to one region.
• Trezor systems were not compromised, and your device is secure.Who is affected:
• If you received our email today and ordered between 9 August and 7 November, your details were part of this incident.
• A small number of customers who ordered between 9 and 14 August may also be affected, but we can’t email them: their details had already been anonymized in our systems.
• Skladon does not ship to the US, so customers there are not affected.Treat any unexpected call, text, email or letter about your order as suspicious, and be alert to potential risks to your physical security. Trezor will never cold-call you or ask for your wallet backup.
From today, anonymous pickup is live in 18 European countries, so you can order without giving us your home address. We’re also shortening our data retention period from 90 days to 45 (and plan to reduce it further), and we’re requiring our shipping partners to follow the same policy.
We’re deeply sorry this has happened.
Full details and FAQs: https://t.co/bU0HAIB5cO
— Trezor (@Trezor) November 16, 2026
Trezor Introduces Anonymous Pickup and Shorter Data Retention
Trezor has announced several changes to reduce the amount of personal information collected and retained during customer orders.
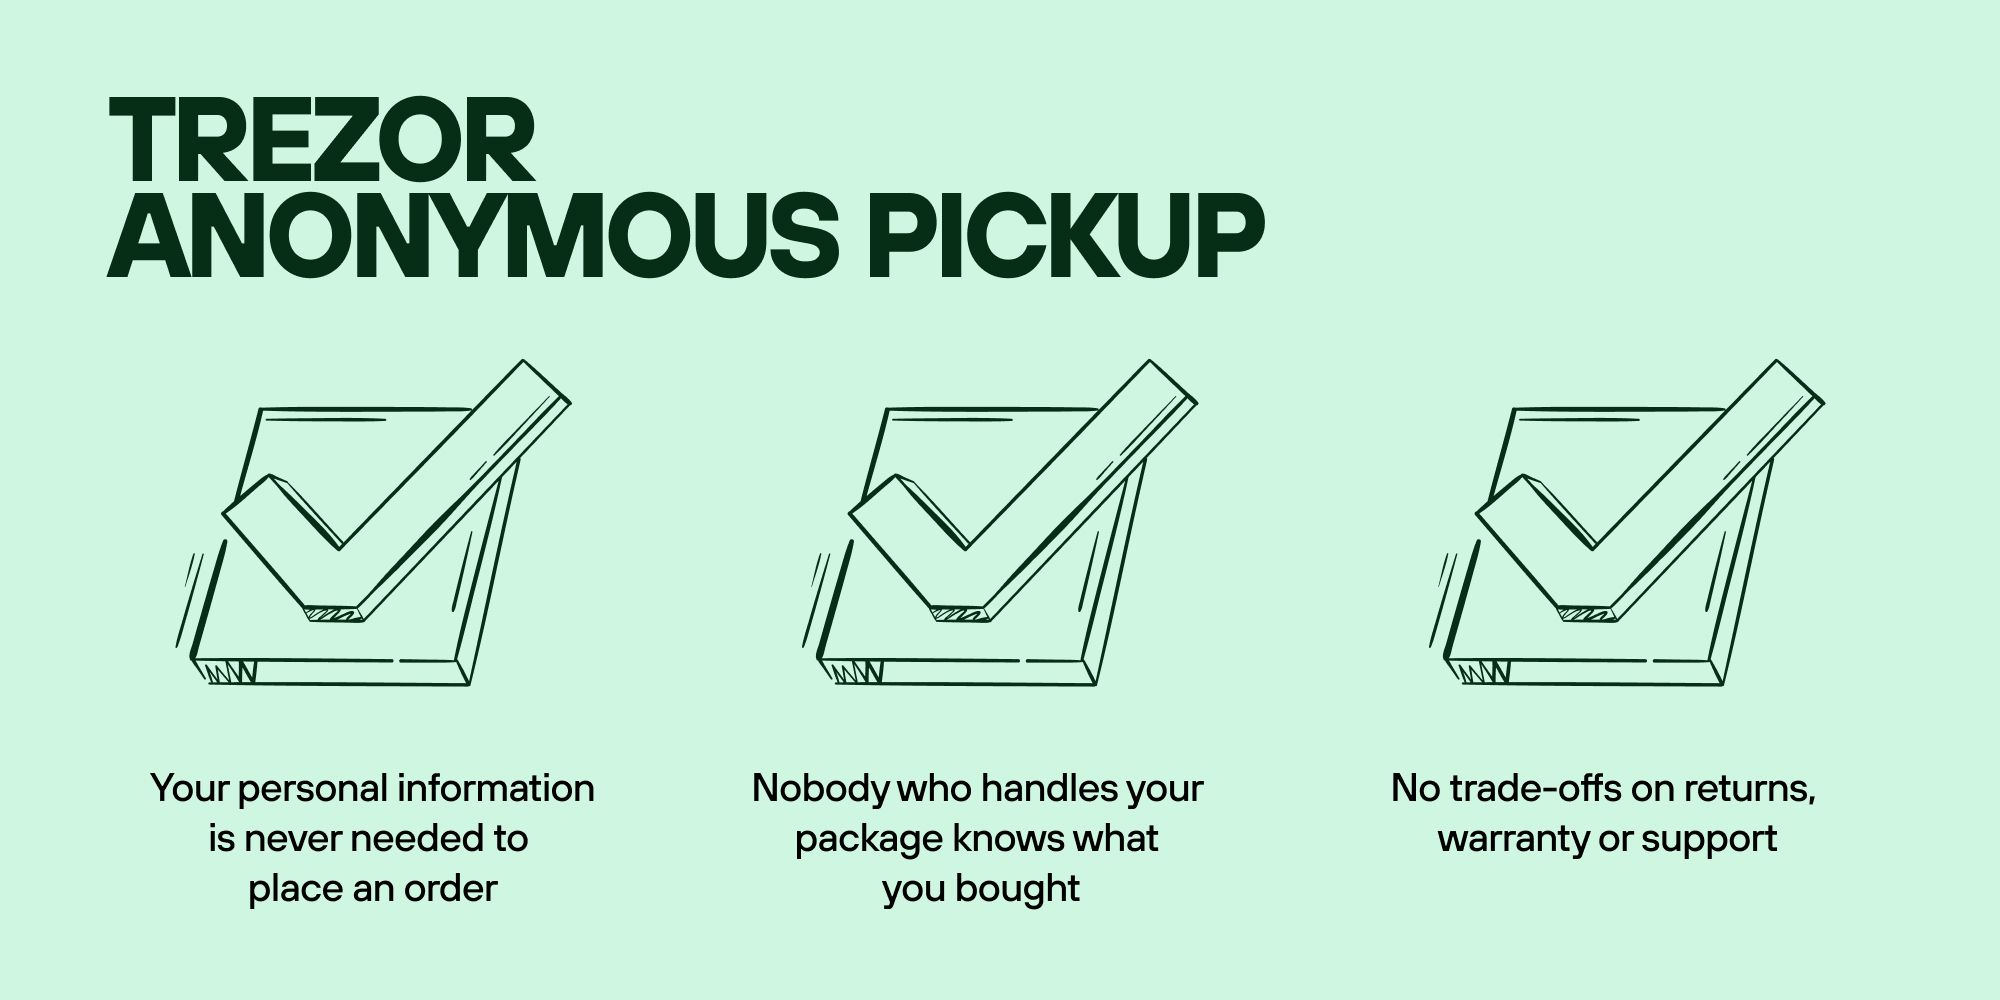
Anonymous Pickup, which the company had been developing since early 2026, is now available in 18 European countries. The service allows customers to collect their hardware wallets from parcel lockers or designated pickup points instead of providing a residential delivery address.
The company is also reducing its order data retention period from 90 days to 45 days, with plans to shorten it further. This change is intended to limit how long customer information remains available within its order processing systems.
Trezor is also reviewing its relationships with third party delivery providers and the security requirements imposed on them. The company has acknowledged that this incident highlights concerns beyond its own infrastructure, particularly the protection of customer information handled by external partners.
Previous Shipping Partner Breach Raises Further Concerns
The Skladon incident is not the first time Trezor customers have faced exposure of personal information through a delivery partner. Trezor acknowledged that customer contact details and residential addresses had previously been exposed in an incident involving another partner.
The company apologized to affected customers and recognized the additional concern for people who have experienced repeated exposure of their information.
Its investigation with Skladon is ongoing. Trezor has also informed the relevant data protection authority and said it will update its official announcement as more information becomes available.
The company has clarified that wallet backups, PINs and passphrases were not involved in the breach. Neither Trezor nor Skladon stores customers' wallet backups.
For affected customers, the immediate concern remains the misuse of exposed contact and delivery information in phishing attempts, fraudulent calls and other targeted scams.
If you find any issues in this article or notice missing information, please feel free to reach out at team@etherworld.co for clarifications or updates.
To promote your Web3 articles, events, and projects, you may reach out anytime via EtherWorld PR for submissions and collaboration.
Related Articles
- Ledger CEO Defends Wallet Security After $90M Hack
- Binance Warns of iOS worse_query Wallet Risk
- Ankr Bridge Exploit Drains $292K in Crypto
- Binance Withdrawal Update After $6.3B Crypto Hack
- Polygon Plans Hard Fork to Recover 70.49M POL
To follow blockchain news, track Ethereum protocol progress, and read our latest stories, subscribe to our weekly today.
Join the EtherWorld & Avarch Internship Program and build your career in blockchain, content, social media, video, podcast editing, or operations. Send your resume and brief introduction to contact@etherworld.co.
Disclaimer: The information contained in this website is for general informational purposes only. The content provided on this website, including articles, blog posts, opinions, & analysis related to blockchain technology & cryptocurrencies, is not intended as financial or investment advice. The website & its content should not be relied upon for making financial decisions. Read full disclaimer & privacy policy.
To stay updated on blockchain news, Ethereum protocol progress, and our latest stories, subscribe to our weekly digest and YouTube channel for ELI5 content.
To promote your Web3 articles, events, project updates, and Press Releases, reach out anytime via EtherWorld PR for submissions and collaboration. For other queries, email contact@etherworld.co.
If you’d like to support our work, share the content and consider donating at avarch.eth.
Join our community on Discord and follow us on Twitter, Facebook, LinkedIn & Instagram.

 ×

Author
Nidhi Kumari is a Web3 content writer at EtherWorld.co, tracking ecosystem developments, funding activity, and market trends shaping the crypto space.