CryptoBilis Ledger Scandal Raises Wallet Security Concerns
Ledger investigates a CryptoBilis hardware implant that steals Ledger recovery phrases through an LTE connection as former founders address the incident.
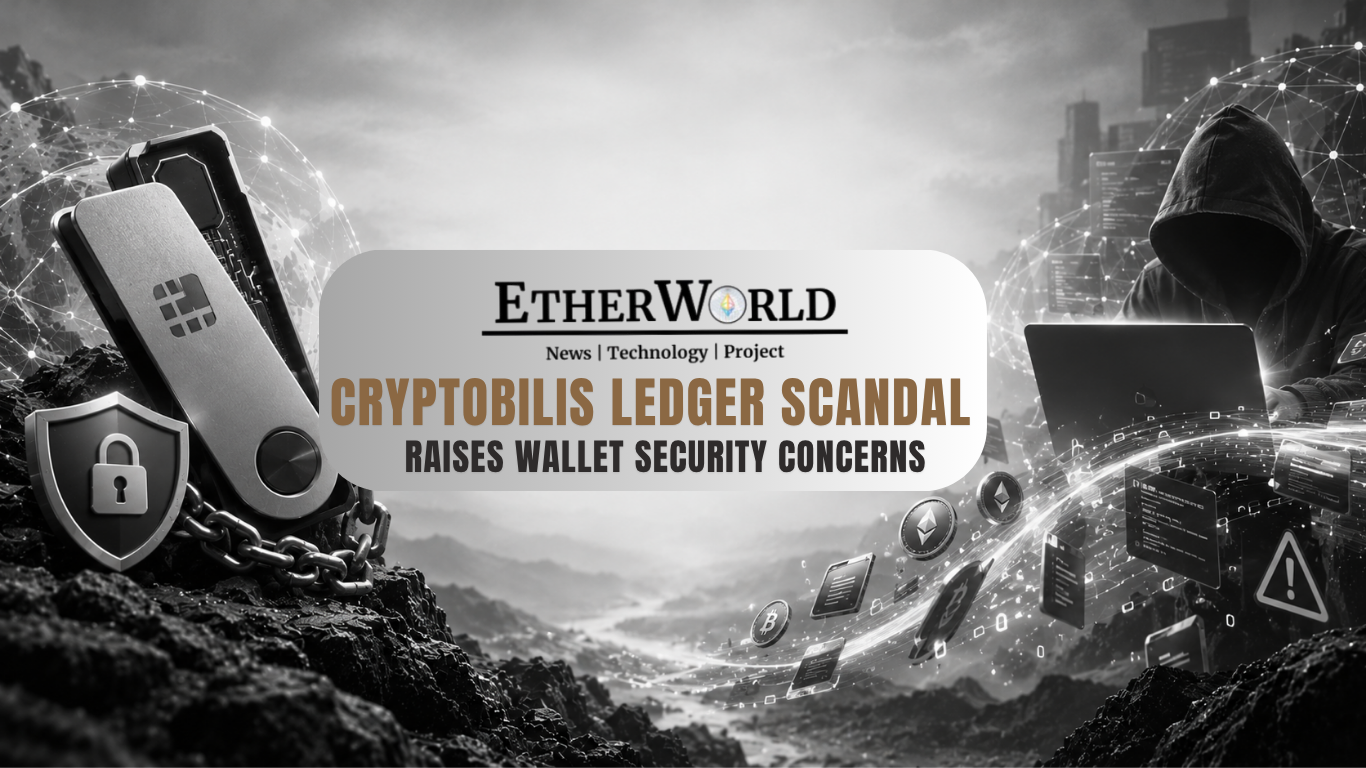
Ledger is looking into cryptocurrency theft linked to Ledger signers that were sold through Southeast Asian reseller CryptoBilis. Ledger's Donjon security team outlined how an unauthorized hardware implant inside an affected device may obtain its 24-word recovery phrase and send it over an LTE connection in an update released on October 13, 2026.
One affected signer has been confirmed by Ledger, however the total amount of stolen money and the number of affected consumers are still unknown. While the inquiry is ongoing, CryptoBilis has ceased selling the devices.
Ledger Investigates CryptoBilis Signers Linked to Cryptocurrency Theft
Ledger confirmed that signers sold through CryptoBilis are responsible for all money losses it has confirmed in relation to the October 9 incident. No bitcoin drain associated with a signer who bought from another seller has been confirmed by the company.
While the inquiry is ongoing, CryptoBilis has confirmed that company has stopped selling Ledger signers. Although it hasn't determined how many devices might be impacted, Ledger is also examining claims of implants involving additional signers and places.
The figures that are making the rounds on the internet regarding the overall amount of money lost are not entirely confirmed by Ledger. In order to include their cases in the investigation, the company is requesting clients who have lost money to get in touch with its support staff.
Read Ledger Investigates $86M Theft Linked to Reseller for additional information about the suspected theft and how it relates to the reseller.
How the Ledger Hardware Implant Steals Recovery Phrases
According to Donjon Ledger's research, the implant reads data from the screen while sitting inside the device enclosure. A Ledger signer shows the user's 24-word recovery phrase during setup. According to reports, the implant recognizes these screens, uses its microcontroller to decode the text, and then uses a supplied eSIM to send the data over LTE.
According to Ledger, the implant is a different piece of hardware. It does not change transactions or signatures, nor does it change the Secure Element or Ledger operating system. Instead, sensitive data that is displayed throughout the setup procedure is the focus of the claimed attack.
An attacker may be able to access the related bitcoin holdings by using a compromised recovery phrase. Customers whose devices were tampered with before to delivery should be especially concerned about the alleged manner.
As the investigation goes on, Ledger Donjon will continue to examine the signers it gets and disclose more results. The entire extent of the incident has not yet been determined by the company.
Update from Ledger Donjon on the CryptoBilis investigation 🔽
@DonjonLedger is investigating Ledger signers sold by CryptoBilis, a reseller in Southeast Asia, that contained an unauthorized hardware implant. Ledger confirmed this on October 10th for one affected user's signer. All confirmed fund losses tied to the incident disclosed on October 9th involve signers sold through CryptoBilis. We have not verified a drain linked to a signer bought elsewhere. CryptoBilis has confirmed it stopped selling Ledger signers while the investigation continues.
Based on the Donjon's analysis of the attack, the implant sits inside the enclosure and reads the data shown on the screen. During setup, the signer displays the 24-word recovery phrase. When the implant detects these screens, its microcontroller decodes the words and transmits them over LTE using a provisioned eSIM. The implant is a separate component. It does not modify the Secure Element or the Ledger operating system, and it does not alter transactions or signatures.
The Donjon will analyze the signers it receives and will share more as the investigation continues.
We have not confirmed the total number of affected users or the total value lost. Figures circulating online come from third parties and Ledger has not fully verified them. If your funds were drained and you have not contacted us, please do so through Ledger Support so we can include your case. We are also reviewing reports of implants in other signers and locations. We will continue to share information as the investigation progresses. Rest assured the Ledger team is going above and beyond to leave no stone unturned to investigate this situation to the strongest possible outcome.
If you bought a Ledger signer from CryptoBilis and have not set it up, do not set it up and contact Ledger Support. If you have set it up, transfer your assets promptly to a new signer with a new recovery phrase. Do not enter or restore any recovery phrase on a signer bought from CryptoBilis. Never enter your recovery phrase into a website, app or form.
If you lost funds or hold a tampered signer, contact Ledger Support at https://t.co/QzukOZdEzq and file a report with local law enforcement. Do not send the signer to anyone before speaking with Ledger Support or local law enforcement. If you lost funds, coordinate with law enforcement before opening the signer. Researchers and others with relevant information can write to security@ledger.com.
If you did not buy from CryptoBilis and want to inspect the inside of your signer, the guide is at https://t.co/Bh9DHQulIv. Use caution and make sure your recovery phrase is backed up first, because opening a signer can damage it.
Ledger will never call you, message you directly, or ask for your 24-word recovery phrase. We will update this post when we verify new information.
— Ledger (@Ledger) October 13, 2026
Former CryptoBilis Founders Address Ownership Change
The founders of CryptoBilis have detached themselves from the Ledger debacle, stating that the company's ownership changed in March 2026. The move coincides with Ledger's investigation into verified bitcoin losses involving signers who were supplied by the Southeast Asian reseller.
A key aspect in determining the business history of the impacted devices is the ownership change. It does not, however, specify who was in charge of the claimed thefts, when the devices were tampered with, or who put the illicit hardware implant.
The entire number of impacted clients and the total amount of stolen cryptocurrencies have not yet been verified by Ledger. The security team is still investigating it, looking at more devices and analyzing allegations of similar implants involving different signers and places.
Ledger Issues Urgent Security Guidance for Affected Customers
Customers who purchased a signer from CryptoBilis but haven't set it up are recommended by Ledger to contact Ledger Support instead of using it. If a customer has previously set up such a device, they should immediately use a new recovery phrase to transfer their assets to a new signer. No recovery phrase should be entered or restored on a signer that was purchased using CryptoBilis.
Additionally, the business has reaffirmed that it would never give clients a call, send them a direct message, or request that they reveal their 24-word recovery phrase. This sentence should never be entered into an online form, application, or website.
Ledger Support should be contacted and local legal enforcement should be notified by anyone who has lost money or has a potentially manipulated signer. Customers are advised by Ledger to contact support or law enforcement before sending the device to anyone. Before opening the signer, those who have lost money should work with police enforcement.
Researchers can send an email to security@ledger.com if they have any pertinent information. The Ledger Donjon device inspection guidance can be accessed by customers who bought their signers elsewhere and wish to examine the device. Ledger advises making sure the recovery phrase is backed up first and cautions that opening a signer can harm it.
If you find any issues in this article or notice missing information, please feel free to reach out at team@etherworld.co for clarifications or updates.
To promote your Web3 articles, events, and projects, you may reach out anytime via EtherWorld PR for submissions and collaboration.
Related Articles
- Samsung Adds USDC to 82M Galaxy Devices
- Abstract Blockchain Shutdown Set for December 2026
- ZachXBT Uncovers Chinese $1B Crypto Laundering Ring
- Ethereum Sepolia Glamsterdam Upgrade Goes Live
- LIBRA & M3M3 Case Dismissed by U.S. Judge
To follow blockchain news, track Ethereum protocol progress, and read our latest stories, subscribe to our weekly today.
Join the EtherWorld & Avarch Internship Program and build your career in blockchain, content, social media, video, podcast editing, or operations. Send your resume and brief introduction to contact@etherworld.co.
Disclaimer: The information contained in this website is for general informational purposes only. The content provided on this website, including articles, blog posts, opinions, & analysis related to blockchain technology & cryptocurrencies, is not intended as financial or investment advice. The website & its content should not be relied upon for making financial decisions. Read full disclaimer & privacy policy.
To stay updated on blockchain news, Ethereum protocol progress, and our latest stories, subscribe to our weekly digest and YouTube channel for ELI5 content.
To promote your Web3 articles, events, project updates, and Press Releases, reach out anytime via EtherWorld PR for submissions and collaboration. For other queries, email contact@etherworld.co.
If you’d like to support our work, share the content and consider donating at avarch.eth.
Join our community on Discord and follow us on Twitter, Facebook, LinkedIn & Instagram.

 ×

Author
Nidhi Kumari is a Web3 content writer at EtherWorld.co, tracking ecosystem developments, funding activity, and market trends shaping the crypto space.